RESEARCHNew from Trench Labs: How Trench Stopped an Agentic Supply Chain Attack Before It SpreadRead Research
BLOGRead our latest blog post: Welcome to Cyber Defense 2.0 - Part 1Read Article
AWARDAnnouncement: Trench Security is the 2026 Winner of ‘Products That Count’Read the Announcement
RESEARCHNew from Trench Labs: How Trench Stopped an Agentic Supply Chain Attack Before It SpreadRead Research
BLOGRead our latest blog post: Welcome to Cyber Defense 2.0 - Part 1Read Article
AWARDAnnouncement: Trench Security is the 2026 Winner of ‘Products That Count’Read the Announcement
RESEARCHNew from Trench Labs: How Trench Stopped an Agentic Supply Chain Attack Before It SpreadRead Research
BLOGRead our latest blog post: Welcome to Cyber Defense 2.0 - Part 1Read Article
AWARDAnnouncement: Trench Security is the 2026 Winner of ‘Products That Count’Read the Announcement
2026 WINNERProducts That Count

The Operating System
for Actionable SecOps.

An agentic platform doing what SIEMs cannot and SOC teams never reach, automatically. Unify your entire security stack so a lean team operates like an enterprise SOC.

Loved by Modern Security Leaders

“Finally a platform built ground up for lean security teams. Trench gives a small team the detection power of an enterprise SOC, without the complexity, without the overhead.”

Senthil Kumar Iyyappan,

CISO, Ocrolus, Ex-Freshworks

AI built for Actionability, not just Visibility.

TRUSTED BY

Securing Forward-Thinking Teams

Trench empowers modern security teams to operate at the speed of AI.

THIS IS YOUR TRENCH

One Agentic Platform: Three Outcomes

Trench unifies your entire security stack into one agentic platform, so your lean team operates like an enterprise SOC.

Visibility

Every signal from every source, unified and searchable from day one.

Velocity

Detection and response measured in seconds, not shifts.

Actionability

End-to-end automated remediation that closes the loop without analyst overhead.
Data Plane

Telemetry OptimizerCollect  →  Normalize  →  Enrich  →  OptimizeData Plane

Control Plane

Agentic SIEMCorrelate  →  Detect  →  Reason  →  PrioritizeControl Plane

Action Plane

Agentic SOCInvestigate  →  Remediate  →  Respond  →  AutomateAction Plane

TASC

(Trench Agentic Schema Context)

Intent Graph

Entity - Behavior - Relationships

Headless SecOps

Autonomous - Always On - No L1/L2

From cognitive overload to cognitive harmony.

Introducing Headless SecOps.

No alerts. No rules. No dashboards. Your SecOps, inside your collaboration tools.

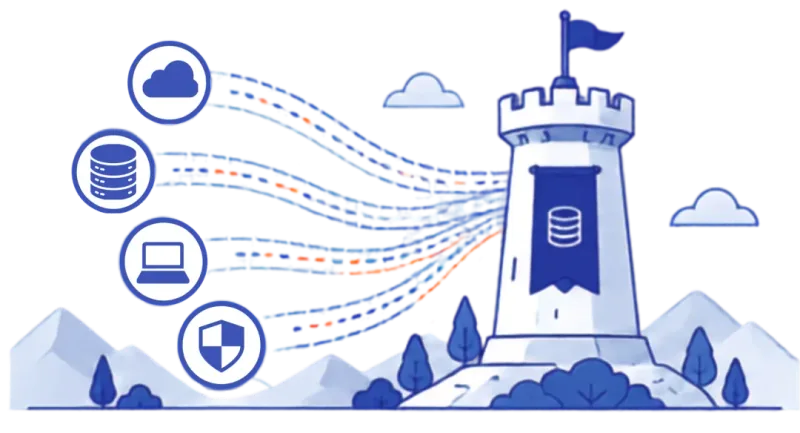
STEP 1, UNIFY

Connect everything. Miss nothing.

Trench connects to every log source, tool and data stream across your stack, cloud, endpoint, identity, network and SaaS. No agents to deploy. No data duplication. Clean, normalized and ready for detection from day one.

Native integrations across your entire stack
Agentless connector-based setup
Auto-normalized, enriched, and searchable
DATA ENGINE
UNIFIED MESH
DATA LAKE
Unified Mesh Data Lake
SEARCHABLE
ENRICHED
NORMALIZED
AGENTLESS SETUP
SOURCES→ENGINE→UNIFIED LAYER

STEP 2, DETECT

Detection driven by intent, not just rules.

Trench's Intent Graph continuously maps attacker behavior, correlates signals across your entire data footprint and auto-generates detections aligned to real-world threats, not static rules written last quarter.

Intent Graph detects based on attacker behavior, not signatures
Real-time threat correlation across your stack
MITRE ATT&CK aligned. Always current.
RAW
SIGNALS
LOG
ALERT
EVENT
FLOW
INTEL
INTENT
GRAPH
LATERAL MOVEMENT
PRIV ESCALATION
DATA EXFIL
C2 COMMS
INITIAL ACCESS
PERSISTENCE
MITRE ATT&CK ALIGNED
AUTO-GENERATED
DETECTIONS
SIGNALS→INTENT GRAPH→DETECTIONS

STEP 3, RESPOND

From alert to closed in minutes.

When a threat is detected, Trench agents automatically investigate, correlate context and trigger response workflows. Your team gets actionable outcomes inside their collaboration tools. No context switching. No cognitive overload.

Automated investigation and triage
Decisions delivered to your collaboration tools
Your team focuses on decisions. Not busywork.
1
THREAT DETECTED
2
AGENT INVESTIGATES
3
CONTEXT CORRELATED
4
RESPONSE TRIGGERED
5
THREAT CLOSED
AI AGENT ACTIVITY
Querying SIEM logs...
Checking identity context...
Mapping blast radius...
Correlating IOCs...
Triggering containment...
RESPONSE METRICS
Detection → Response< 5 min
Alert → Closed< 10 min
Human ReviewDecisions only
CoverageFull stack
DETECT→INVESTIGATE→CORRELATE→CLOSE

How Trench Works Inside Collaboration

We bring SecOps to where you work.

From detection to remediation, inside Slack, Teams, or Claude.

01

Detect

Suspicious sign-in flagged with full context.

02

Verify

Trench asks the impacted user, in DM.

03

Approve

Security engineer is paged for one-click approval.

04

Remediate

Tokens revoked, sessions killed, ticket closed.
Trench
you
Channels
#general
#sec-ops
#incidents
#detections
#eng-platform
Apps
TTrench
#sec-ops
Live security operations | 12 members
Trench | live
TrenchAPP10:42 AM
🚨 Suspicious sign-in detected for @maya.chen
SourceOkta + CrowdStrikeLocationLagos, NG | impossible travel from Berlin (4 min ago)Deviceunmanaged | new fingerprintRiskHIGH | 0.91
Reaching out to @maya.chen in DM to verify…
Trench is typing…
TrenchSTEP 2: VERIFY10:43 AM
Sent a verification DM to @maya.chen:
↳ DM to @maya.chen
Hey Maya, we noticed a sign-in to your account from Lagos, NG on an unmanaged device a few minutes ago. Was that you?
👍 Yes, it's me
🚫 Not me
MC
Maya Chen10:44 AM
🚫Not me, I'm in Berlin, on my laptop right now.
TrenchSTEP 3: APPROVE10:44 AM
User confirmed compromise. @on-call-secops. Proposed remediation ready for approval:
Proposed actions (3)
Revoke all active Okta sessions for maya.chen
Force MFA re-enrollment + password reset
Block source IP 102.89.34.221
✓ Approve all
Modify
Open in Trench
Trench is typing…
TrenchSTEP 4: DONE10:45 AM
✅ Remediation complete. Account secured in 3m 12s.
Okta sessions revoked12 sessions✓MFA re-enrollment forcednext sign-in✓Source IP blocked102.89.34.221✓Incident filedINC-2148 | Jira↗
Full timeline + evidence saved to INC-2148. Closing the loop here. 🛡️
Message #sec-opsBI@📎

The Trench Principle

No alerts. No rules. No dashboards.

Your SecOps lives inside the collaboration tools your team already uses: Slack, Teams, or Claude. Security without the context switch.

Every Castle Needs a Trench.

Our Trench Protects Your Castle.

The Agentic Operating System for your security stack: protecting everything you have built, 24/7.

Dig In
Trench protects your castle

Community

BlueTeam Premier League

An exclusive cybersecurity league, organised by Trench, where blue teams compete through ideas, strategy and collaboration rather than on a playing field.

Explore the League

Network with Leaders

Directly connect and engage with CISOs, security directors, and industry pioneers in an informal, low-pressure setting.

Exchange Real SOC Experiences

Share war stories, incident response blueprints, and practical orchestration strategies from live production networks.

Sports League Theme

Enjoy a premier fantasy league format with championship trophies, structured gamified modules, and friendly competitive spirit.

Got Questions?

We thought you might.

Trench is an AI-native SIEM platform with built-in agents for cloud-native security teams. It unifies data ingestion, threat detection, investigation, hunting and response into one platform, replacing the manual workflows and legacy tools that slow your team down.

Yes. Trench seamlessly integrates into your security stack working alongside your existing SIEM or replacing it entirely. Agentlessly connecting across cloud, endpoint, identity, email, network, and SaaS tools.

Yes, completely. Trench handles ingestion, detection, and response in one AI-native platform. Most teams are fully operational within 2 weeks at half their current SIEM cost. The platform is compliance friendly for your regulations and auditors.

Traditional rules are written once and go stale fast. Trench's Intent Graph continuously maps attacker behavior across your environment, auto-generating, tuning, and deploying detections in real time. Your team reviews. The Mesh layer of agents do the rest.

That's exactly who Trench is built for. A lean team running Trench gets the detection coverage, investigation depth, and response speed of an enterprise SOC, without the headcount, service provider, complexity, or cost.

SUBSCRIBE TO TRENCH DIGEST